Cryptography
学习笔记 Manning Real-World Cryptography by David Wong
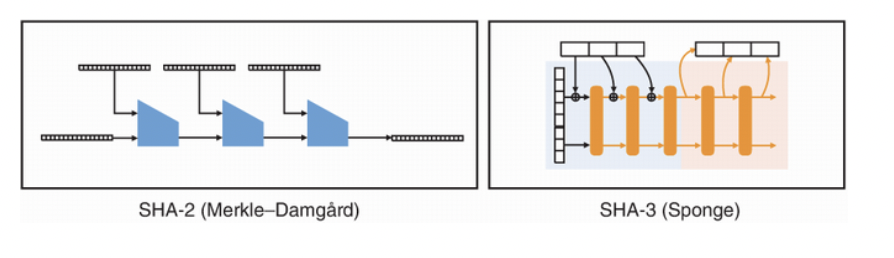
SHA-2
分片-> 递归压缩
SHA-3
Keccak 随机排列(permutation)
定长攻击
利用Sha-256的Padding
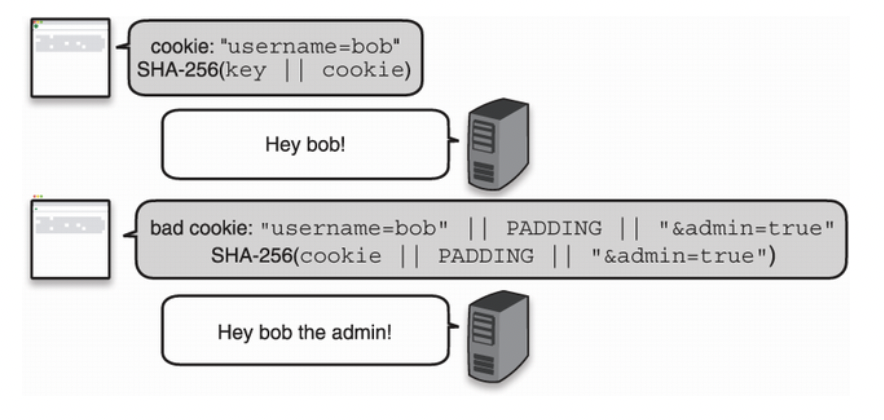
解决方法: HMAC
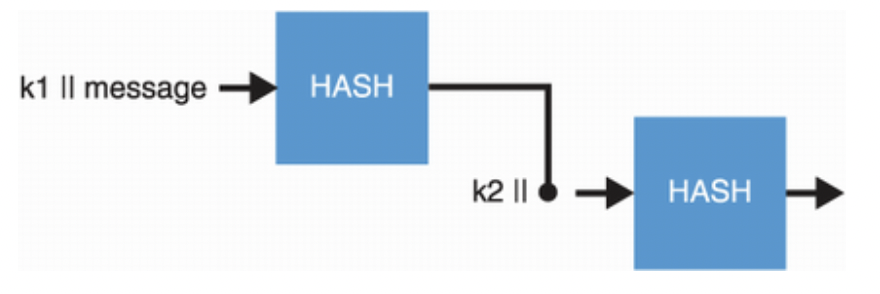
SHA-3不会有Length-extension attack,用KMAC
AES
Block cipher:输入128bit 输出128bit,是可逆的,也是一种permutation
128bit,也就是16byte。转换成一个4x4的矩阵
每一轮都要执行一次round function
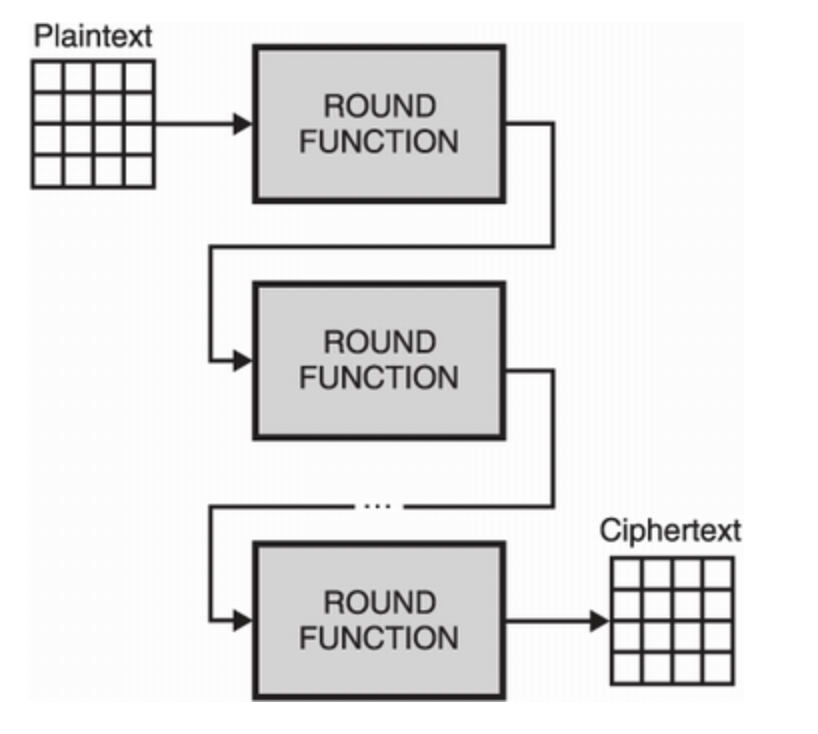
每个round function的过程:
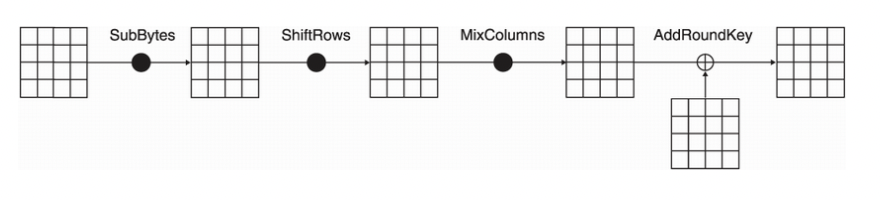
前三步都是可逆的(都是permutation),最后一步XOR RoundKey是不可逆的
PKCS#7 padding
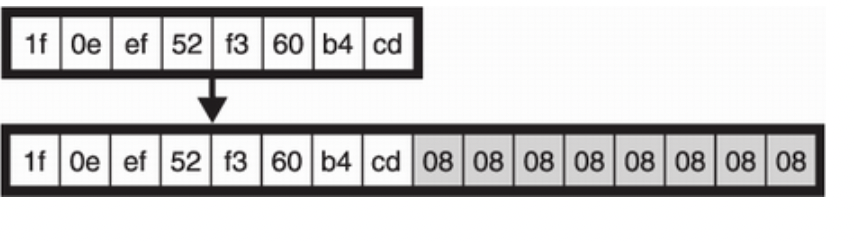
最后n个bit用value n 表示。如果正好整除,用一整个block (blocksize)表示
费马-欧拉定理 与rsa
而欧拉素数函数所以
公钥是 且 与 互素
私钥是
已知,则
已知
因此
这个式子展开等于
后面每一项都有N
所以这个式子
是不是很神奇!
零知识证明
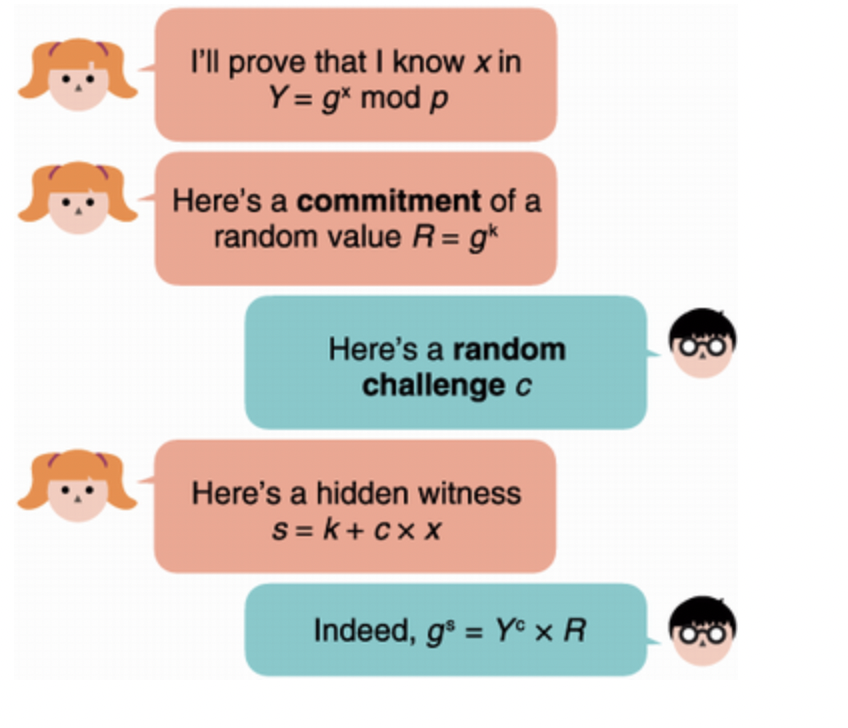
commit, challenge, proof
Randomness
Forward secrecy 知道现在的值,无法倒推回过去的值
Backward secrecy 知道现在的值,无法预测未来的值
Handshake, post handshake
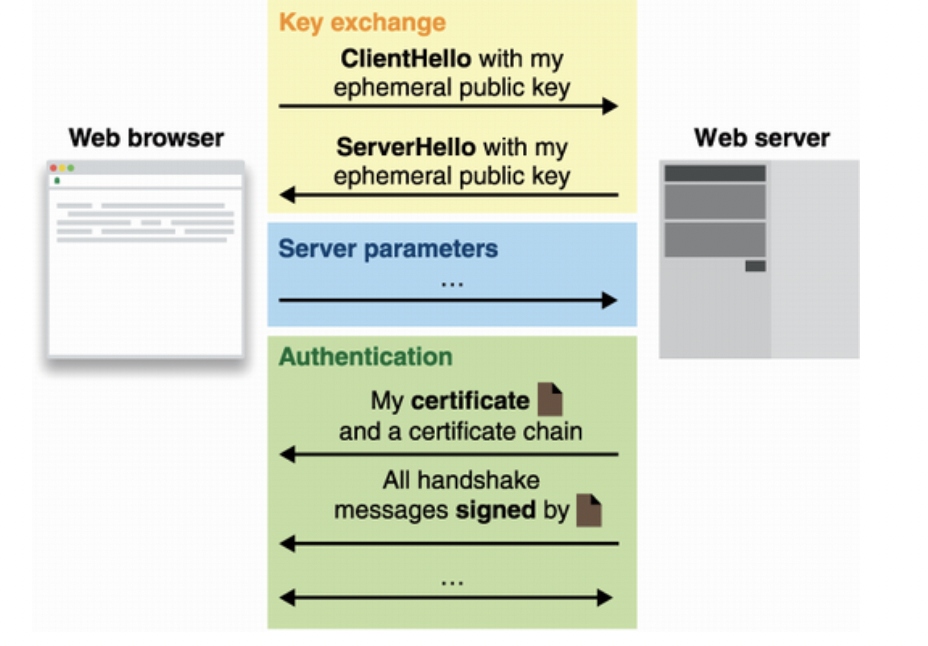
Handshake: key exchange
Post-handshake: message excrypting
客户端向服务端发送 ClientHello,包含一系列支持的SSL和TLS版本,加密算法。
1个或多个密钥交换算法:ECDH,FFDH
2个签名算法:RSA PKCS#1 v1.5 RSA-PSS
1个或多个哈希函数,提供给HMAC和HKDF使用 SHA-256 SHA-384
1个或多个加密算法 AES-GCM, AES-CCM ChaCha20-Poly1305
Ephemeral 客户端和服务端在交换完密钥后,立即销毁。
X509 certificate
使用了ASN.1 language
包含三个部分:
tbsCertificate—The to-be-signed certificate. This contains all the information that one wants to certify. For the web, this can contain a domain name (google.com, for example), a public key, an expiration date, and so on.
signatureAlgorithm—The algorithm used to sign the certificate.
signatureValue—The signature from a CA.
PSK
pre-shared keys
如:两台机器不连到公网,只是相互连
OTP authenticator
one-time password
不想让用户知道了密码,就能无限登录
如:github authenticator
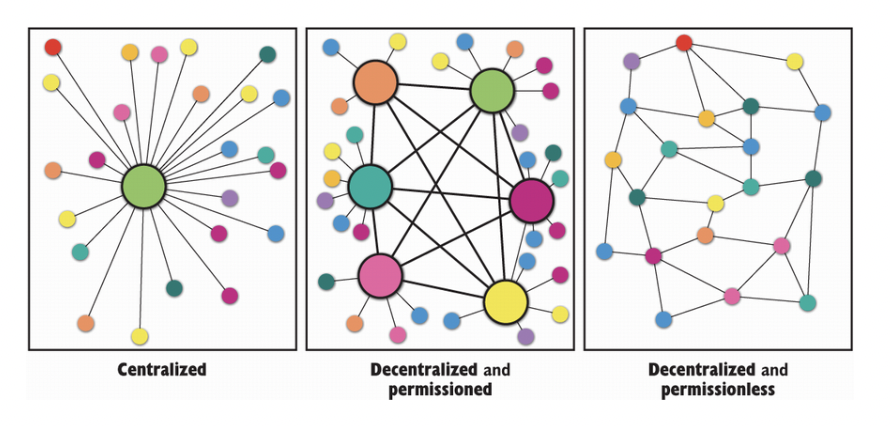
BFT concensus
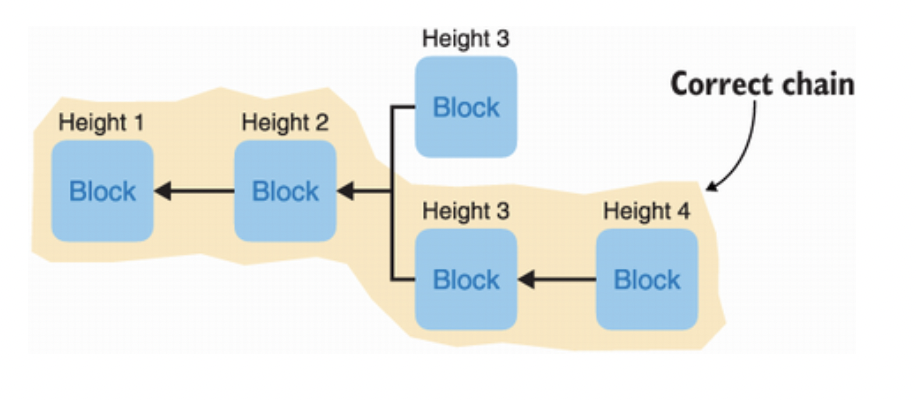
Chain-fork 所以一般transaction需要多个block confirmation。confirmation越多,这个block所在的链越长,越小的可能被其他更长的链取代。
Schwartz-Zippel lemma
两个n度的多项式最多有n个交点
zk-snarks
假设我需要证明我知道f(x)的两个根x1和x2
f(x) = (x-x1)(x-x2)h(x)
我们的目标是既证明了知道f(x)的根,又不给出f(x)。
Homomorphic commitments
Bilinear pairings
“different polynomials evaluate to different values most of the time”